Web app pentest with a signed report, in 5 days.
Has a big client or an auditor asked your company for a pentest report? We test your web app and API, prove every finding and show your team how to fix it. A certified tester signs the report.
€2,500 fixed · 5 working days · retest included
Book a free 30-min call Prefer to talk now? +48 517 773 822Made for a fictional app, so you can see the exact format before you talk to us. No email needed.
Your big client wants proof. A scanner report rarely gives it.
Large companies often ask their software suppliers for an independent penetration test before they sign. You need a report they can read, and a clear plan for anything it finds.
Scope
A 30-minute call on who needs the report and what they expect. You get a fixed scope and price in writing.
Test
AI agents map your app and API and try common attacks. A certified tester then checks roles, tenant separation and business logic by hand.
Prove
Every finding is reproduced by the tester, with the exact request, the response and the impact. False alarms are removed.
Fix
Your developers get a fix for each finding. We retest and give you a signed report and a letter you can share.
Attacks are getting faster
Exploited vulnerabilities are now the most common way into a company, at 31% of breaches (Verizon DBIR 2026). Anthropic reported a state-sponsored campaign against about 30 targets where AI did 80–90% of the work (Anthropic). Most AI-assisted attackers still rely on known techniques, so finding and fixing known weaknesses early is worth doing.
See the report before you book.
A scanner gives you a list of possible issues. We give you proof that each issue is real, what it means for the business and how to fix it.
Possible issues found: 3

[medium] Possible missing rate limit
         /api/v2/auth/login
[info]   Possible IDOR, manual review advised
         /api/v2/invoices/{id}
[info]   X-Powered-By header present
F-03 · High · CVSS 7.7
A user of tenant A can read tenant B's invoices.

curl api.example.com/api/v2/invoices/88213 \
  -H "Authorization: Bearer <tenant A token>"
200 OK  {"tenant":"tenant-b", ...}

Fix: filter the query by tenant_id.
Retest: fixed, now returns 404.
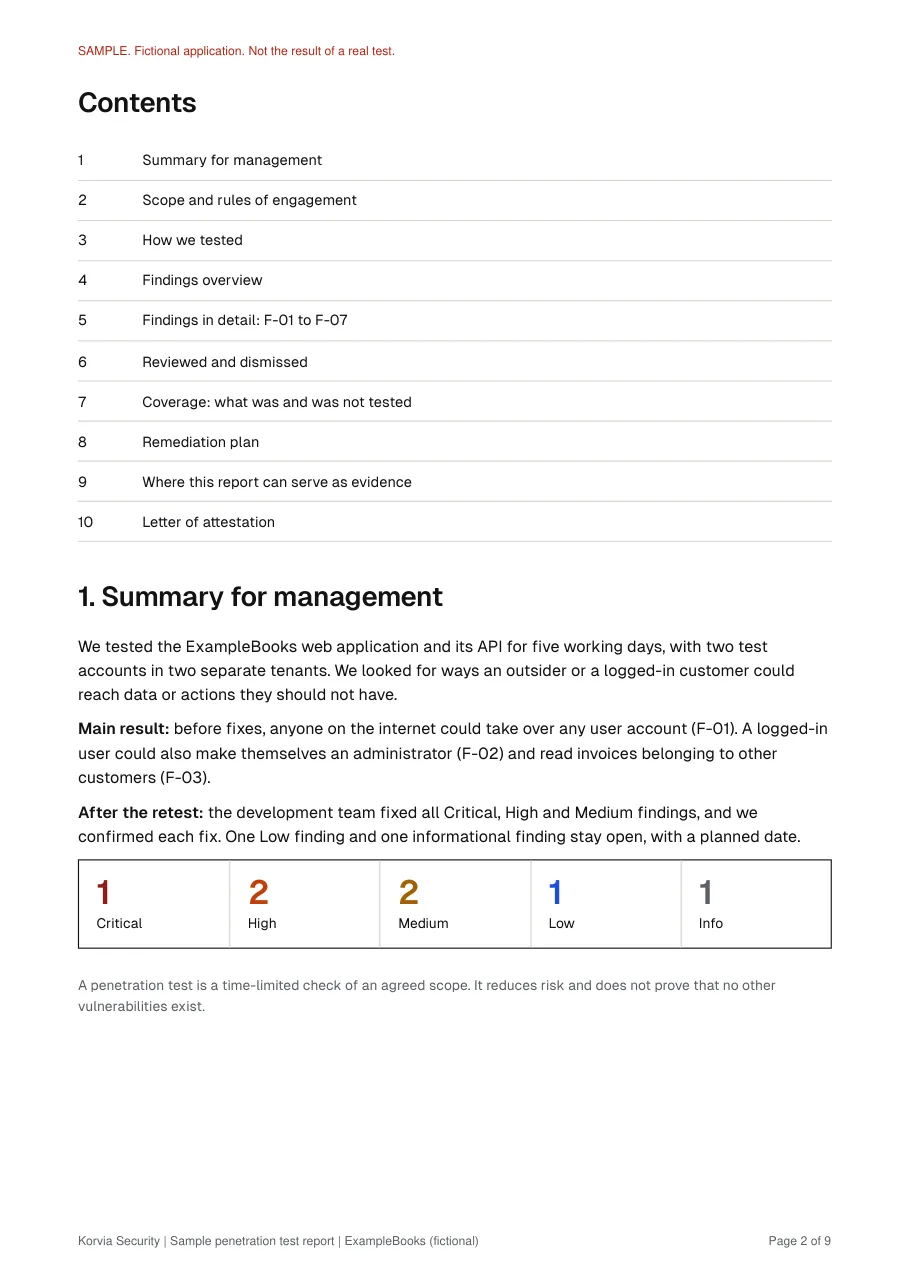
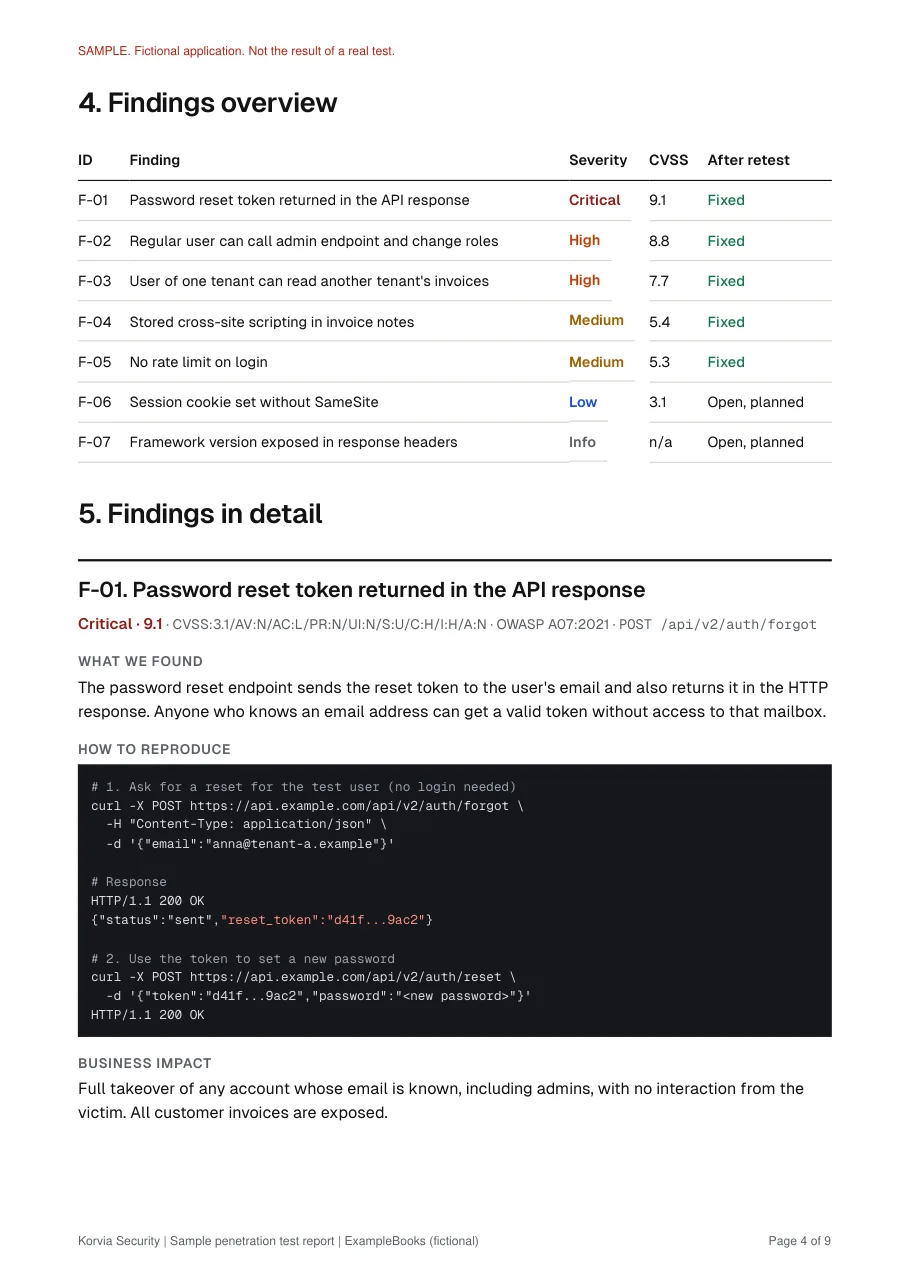
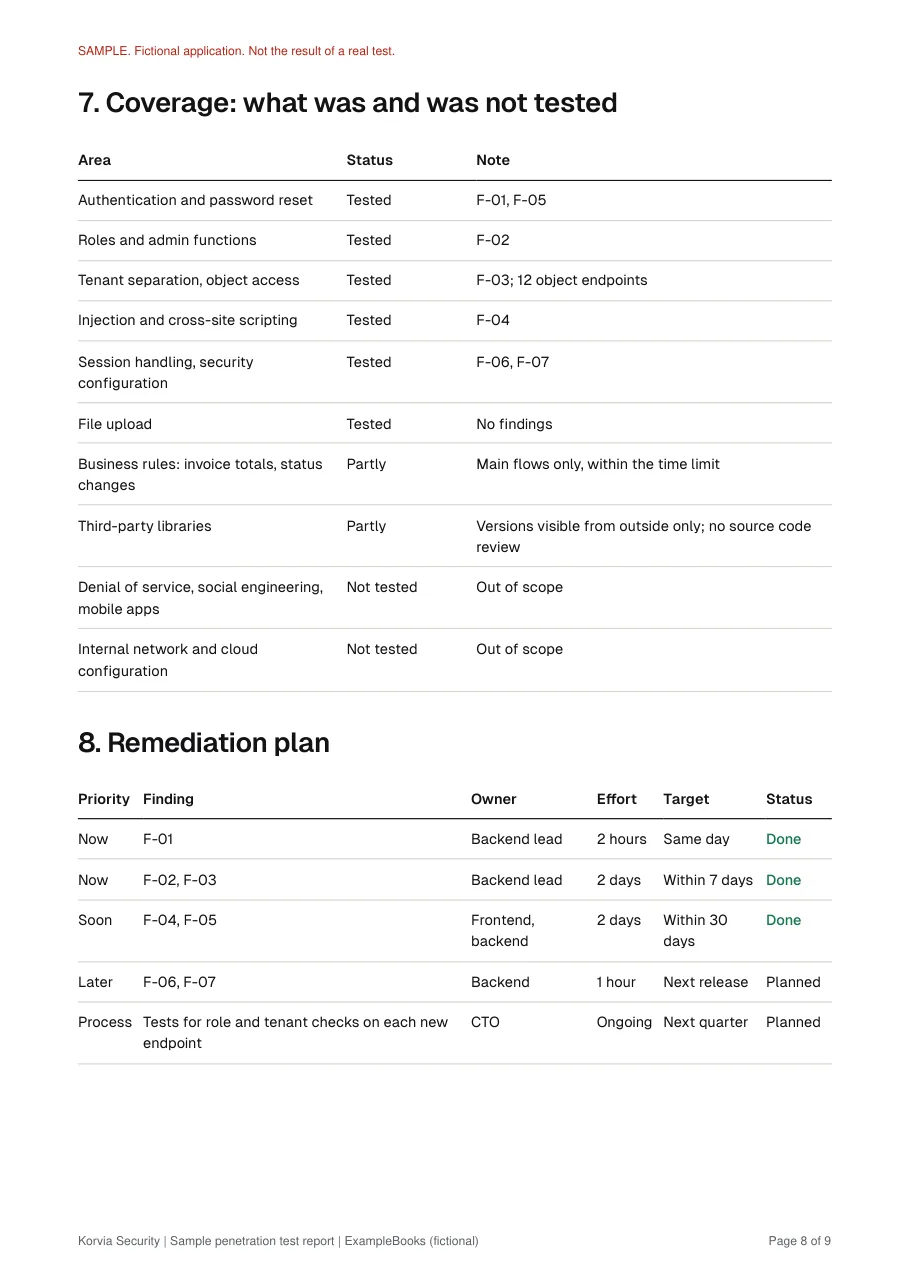
Download the sample report (PDF)
The sample also includes the items we dismissed as false alarms and the letter of attestation you can send to a client. It describes a fictional app: no real system was tested.
One app, 5 working days, a fixed price.
We work on a staging copy where possible, and only after you sign a written authorisation.
Scope and authorisation
Written scope, NDA and authorisation. You give us URLs and two test accounts. We don’t need your source code.
AI-assisted first pass
Mapping the app and API, then common attacks at agreed rates and inside the agreed scope.
Manual testing
The tester reproduces each candidate and tests roles, tenant separation, password reset and business rules.
Report and walkthrough
Full report and a 30-minute call with your developers. We tell you at once if we find something critical during the test.
Retest and letter
- Each fix checked again, with the result in the report
- Signed final report
- Letter of attestation to share
Security Review
1 web app with its API, 1 user role, retest included.
- Payment
- 50% at the start, 50% when you receive the report.
- Your tester
- OSCP or OSWE certified. You get the name and certificate before you pay.
- Start date
- Agreed on the call. If we can’t start on that date, you get a full refund.
- Not promised
- No test can find everything. The report states what was and wasn’t tested.
If you need more
Security Review Plus
Up to 3 user roles, a larger API and more time on business logic. Retest included.
Help with fixes
Work with your developers on the fixes, in your stack, after the report.
Quarterly retest
A new test of what changed, with an updated report and letter for your clients.
Prices excl. VAT. Invoiced in EUR from Poland; EU VAT rules apply.
Who you’ll work with
Mikhail Mukhanov runs Korvia Security: scope, contract and delivery
Mikhail has 15 years of experience in data systems and delivery for retail, FMCG, fintech, pharma and manufacturing companies. He is your contact from the first call to the final report.
The testing and the sign-off are done by a certified penetration tester (OSCP or OSWE). You get the tester’s name and certificate before you pay.
Korvia Security is a new service, so we show you a sample report and not a client list.
Who this is for.
Good fit
- SaaS and AI companies whose client sent a security questionnaire
- Teams preparing for ISO 27001 or SOC 2
- Software houses asked for proof of testing by a client
- IT suppliers to banks and fintechs
- Companies with no security team that want help from scope to fix
Not a fit
- A formal KSC or NIS2 audit: that needs qualified auditors
- PCI DSS tests or tenders that require CREST
- Red-team exercises and DORA TLPT
- Public tenders that require a report in Polish
- Testing any system you don’t own or have no right to authorise
Before you book.
Will my auditor or client accept this report?
They make that decision, so we can’t promise it. Send them the sample report before you pay and ask. If they need something specific, tell us on the call and we’ll say whether we can provide it.
How do you use AI, and where does our data go?
AI agents do the first pass and suggest candidates. A person confirms each finding and does the logic testing. Every provider that handles test data is named in the data processing agreement before we start. If your rules don’t allow an outside AI provider, tell us on the call.
Could the test break our app?
Any active test carries some risk, including on a well-run system. That’s why we prefer a staging copy with test data, keep to agreed rates, avoid denial-of-service testing and agree a stop contact. If production is the only option, we plan the window with you and check that you have backups.
How is this different from a scanner or a self-serve AI pentest?
Scanners list possible issues. Self-serve AI tools are good and often cheaper, and if your team can run one and its report is accepted, you may not need us. We suit teams who want a person to agree the scope, name the tester, explain the findings and help with the fixes.
What if you find nothing serious?
The price stays the same, because the work is the same. You still get a report showing what was tested and how, which is what a client or auditor usually wants to see.
What do you need from us?
A signed authorisation from someone entitled to give it, URLs, two test accounts and one technical contact. If you host on a cloud provider, we check its testing rules with you first.
Is this a NIS2 or KSC audit?
No. A KSC audit is done by qualified auditors and covers your whole security management system. A penetration test can feed into your own assessment of whether your security measures work.
How do contracts and invoicing work?
A short services agreement with an NDA, a written authorisation and, if personal data may be reached, a data processing agreement. We invoice in EUR from Poland; EU VAT rules apply. 50% at the start, 50% when you receive the report.
Where are you based?
Warsaw, Poland. We work remotely, in English, with companies across Poland and the EU.